Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = drift75
Pass the SailPoint Professional Identity-Security-Administrator Questions and answers with ExamsMirror
Exam Identity-Security-Administrator Premium Access
View all detail and faqs for the Identity-Security-Administrator exam
0 Students Passed
0% Average Score
0% Same Questions
Does this statement accurately describe the purpose of the Virtual Appliance (VA)?
Proposed Solution / Statement:
The VA eliminates the need for databases to store Personally Identifiable Information (PII).
Does this proposed solution meet the requirement / solve the scenario?
Below are the requirements for configuring user provisioning in an organization's Finance department.
Contractors in the organization MUST NOT be auto-provisioned with the default Office 365 license, as contractors in departments other than Finance have different license requirements.
Every Finance department user — whether employee or contractor — must be assigned one Office 365 E3 license.
No Finance employee or contractor should be provisioned more than one type of Office 365 license.
Is this a valid approach for the Identity Security Administrator to provide the necessary access?
Proposed Solution / Statement:
Create an ISC Role with membership criteria that includes all Finance department contractors. Assign an Access Profile associated with the default Office 365 license. Add these users to the Office 365 E3 license entitlement so they receive an account with the default Office 365 license and the required E3 license.
Does this proposed solution meet the requirement / solve the scenario?
An organization must maintain both production and sandbox tenants of Identity Security Cloud. The administrator needs to maintain consistent configurations across both environments, and backup and restore from previous configuration backups.
Does the following statement accurately describe how Configuration Hub functionality can help in this scenario?
Proposed Solution / Statement:
Configuration Hub allows one to create configuration templates that can be exported and imported across tenants.
Does this proposed solution meet the requirement / solve the scenario?
An Identity Security Cloud tenant is configured to disable all source accounts for an identity that enters the terminated lifecycle state. A database administrator reports they have been noticing that employees who are terminated, still have their database accounts as "Active" in the source system.
Is this a valid troubleshooting option for the scenario above?
Proposed Solution / Statement:
On the Identity, validate that the Lifecycle State attribute value that is set for the affected users is "Terminated".
Does this proposed solution meet the requirement / solve the scenario?
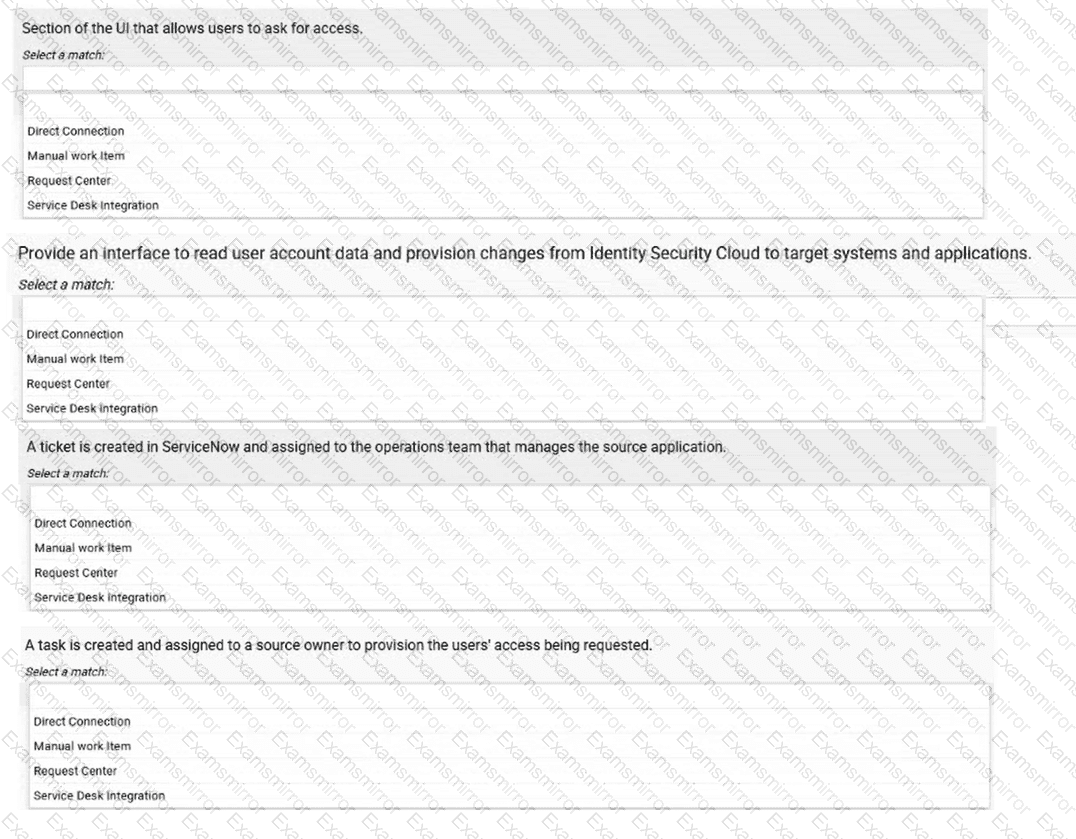
Match the following descriptions with their appropriate definition.

Users are complaining that they would like to request access to groups that have recently been added to the Corporate Directory system, but they are unable to see them. The system feature Enable Entitlement Requests has been enabled and access request segments have not been enabled.
Is this a valid step to debug the problem?
Proposed Solution / Statement:
Open the source configuration and navigate to the Access Profiles page to check if the group is included in it and thus hidden by any Access Profile.
Does this proposed solution meet the requirement / solve the scenario?
Is this a valid way to set-up role assignment criteria?
Proposed Solution / Statement:
A list of Excluded Identities can be defined to prevent specific identities from receiving the role membership.
Does this proposed solution meet the requirement / solve the scenario?
A legacy custom-built application, which contains contractor information used by HR, must be integrated with the Identity Security Cloud (ISC) solution as the authoritative source.
Is the following a valid point to consider regarding the integration?
Proposed Solution / Statement:
Generic connectors (such as delimited file or JDBC) can be used to integrate the legacy custom-built application.
Does this proposed solution meet the requirement / solve the scenario?
An organization is considering purchasing an IGA tool. The manager asks the administrator to explain what compliance features the IGA tool provides for separation of duties, protecting personally identifying data and privileged access, and how the company can prove to the auditors that they comply with all laws and regulations.
Is this a good explanation of one of such features?
Proposed Solution / Statement:
"Separation of duties can be enforced using rules that can be configured in the system. These rules look for forbidden combinations of access owned by a single user. The rules can be used in a detective way, meaning actively searching for these forbidden combinations, or a preventative way, meaning that an extra validation step is made when a change in user access is requested."
Does this proposed solution meet the requirement / solve the scenario?
Does the following event trigger the de-provisioning of a user's access?
Proposed Solution / Statement:
The department of a user changes, and the new department does not have access to an application that was previously assigned.
Does this proposed solution meet the requirement / solve the scenario?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.