Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = drift75
Pass the Fortinet NSE 6 Network Security Specialist NSE6_FSM_AN-7.4 Questions and answers with ExamsMirror
Exam NSE6_FSM_AN-7.4 Premium Access
View all detail and faqs for the NSE6_FSM_AN-7.4 exam
0 Students Passed
0% Average Score
0% Same Questions
Refer to the exhibit.

An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add Destination Host Name as an incident attribute.
What must be changed to allow the analyst to select Destination Host Name as an attribute?
Refer to the exhibit.

A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword " udp " . However, they are getting no results from the search, which they know should be available. Based on the filter shown in the exhibit, why are there no search results?
Refer to the exhibit.

Which value would you expect the FortiSIEM parser to use to populate the Application Name field?
Refer to the exhibit.

According to the automation policy configuration shown in the exhibit, what happens if an associated rule triggers?
Refer to the exhibits.


Three events are collected over 10 minutes from two servers: Server A and Server B.
Based on the settings for the rule subpattern and a 10-minute condition window, how many incidents will the servers generate?
Refer to the exhibit.
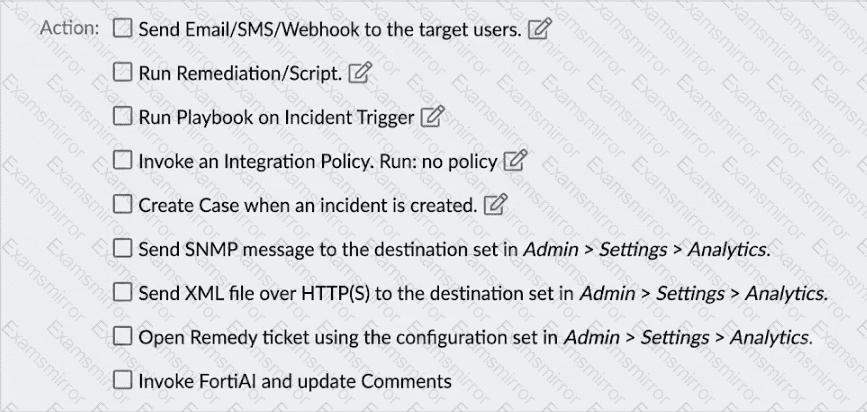
Which two actions can you select in an automation policy to trigger an API call to block an IP address on a FortiGate? (Choose two.)
What are two required components of a rule? (Choose two.)
Refer to the exhibit.
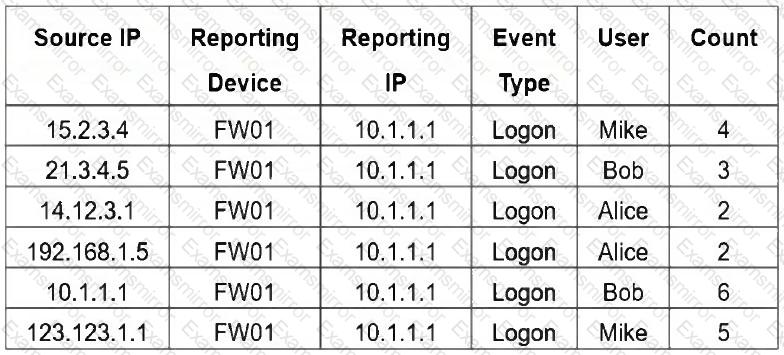
If you group the events by User , Source IP , and Count attributes, how many results will FortiSIEM display?
You want to create a rule with multiple subpatterns but trigger an incident only if three different subpatterns are matched over a 24-hour period.
Where must you define the time period that the rule uses to evaluate all the subpatterns? (Choose one answer)
Refer to the exhibit.
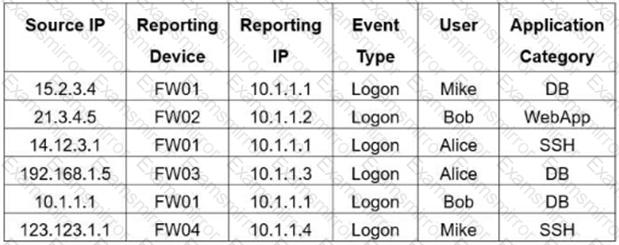
If you group the events by Reporting Device , Reporting IP , and Application Category , how many results will FortiSIEM display?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.