Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = drift75
Pass the Microsoft Certified: Cybersecurity Architect Expert SC-100 Questions and answers with ExamsMirror
Exam SC-100 Premium Access
View all detail and faqs for the SC-100 exam
722 Students Passed
84% Average Score
98% Same Questions
Your company plans to move all on-premises virtual machines to Azure. A network engineer proposes the Azure virtual network design shown in the following table.
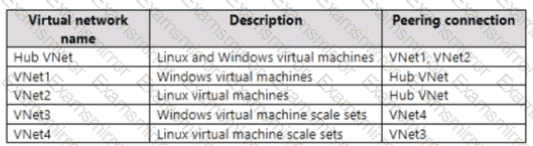
You need to recommend an Azure Bastion deployment to provide secure remote access to all the virtual machines. Based on the virtual network design, how many Azure Bastion subnets are required?
You have an Azure subscription that contains Azure App Service web apps. The apps have the following characteristics:
• The apps are deployed by using continuous integration and continuous deployment (CI/CD) pipelines in Azure DevOps.
• The apps are deployed to a test environment first, and then to a production environment.
• The source code for the apps is stored in Azure Repos.
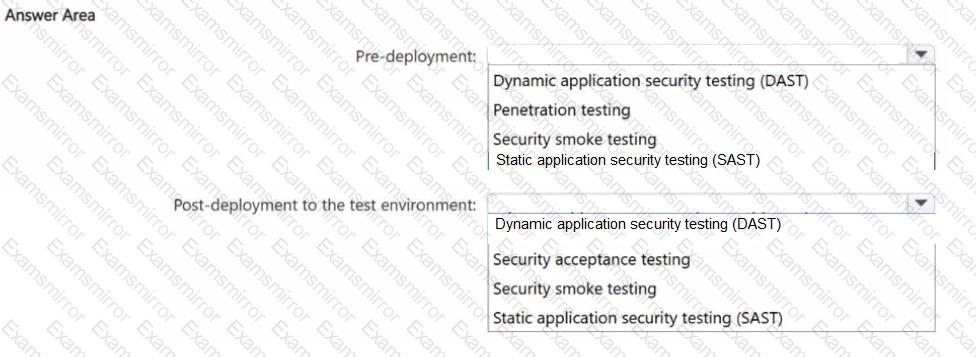
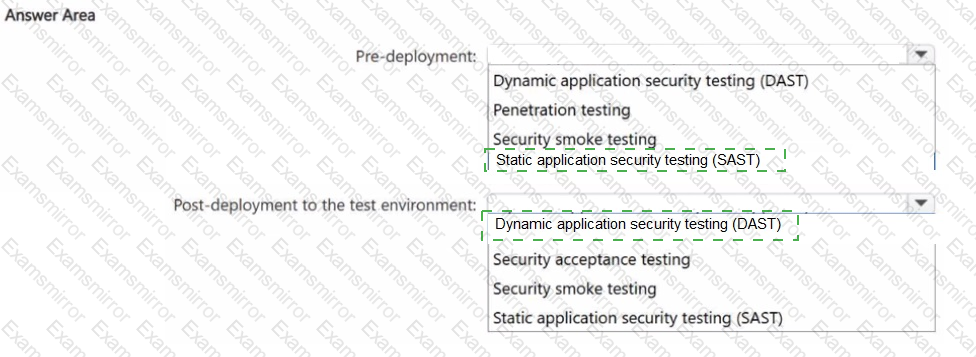
You plan to implement DevSecOps controls based on the Microsoft Cloud Adoption Framework for Azure. You need to recommend testing controls to meet the following requirements:
• All the source code must be tested for security vulnerabilities in Azure Repos before deploying the apps.
• Once the apps are deployed to the test environment they must be tested for security vulnerabilities.
Which testing method should you recommend for each stage? To answer, select the options in the answer area.
NOTE: Each correct answer is worth one point.
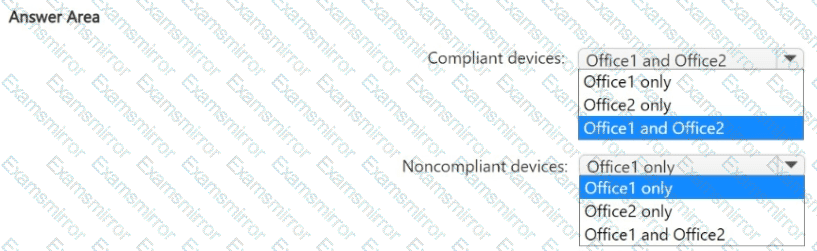
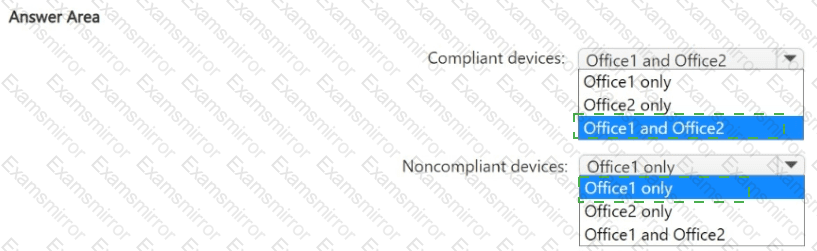
Your company has two offices named Office1 and Office2. The offices contain 1,000 on-premises Windows 11 devices that are Microsoft Entra joined.
You have a Microsoft 365 subscription and use Microsoft Intune.
You plan to deploy Microsoft Entra Internet Access from the offices to Microsoft 365.
You enable the Microsoft 365 profile and configure the following:
• A traffic policy for all Microsoft 365 traffic
• A linked Conditional Access policy that has the following configurations:
° Applies to all users
° Performs compliant network checks
o Allows Microsoft 365 traffic from compliant devices
• An assignment to all devices
• An assignment to the remote network associated with Office1
You deploy the Global Secure Access client to all the devices in Office2 and establish connections.
Which users can access Microsoft 365 services from compliant devices, and which users are blocket1 from accessing Microsoft 365 services when using noncompliar devices? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
A customer has a Microsoft 365 E5 subscription and an Azure subscription.
The customer wants to centrally manage security incidents, analyze log, audit activity, and search for potential threats across all deployed services.
You need to recommend a solution for the customer. The solution must minimize costs.
What should you include in the recommendation?
Your company has a hybrid cloud infrastructure.
Data and applications are moved regularly between cloud environments.
The company ' s on-premises network is managed as shown in the following exhibit.
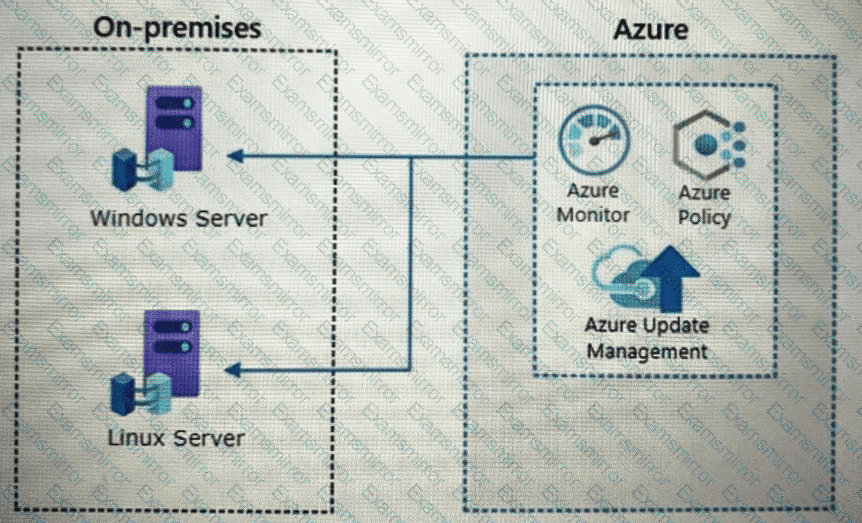
You are designing security operations to support the hybrid cloud infrastructure. The solution must meet the following requirements:
Govern virtual machines and servers across multiple environments.
Enforce standards for all the resources across all the environment across the Azure policy.
Which two components should you recommend for the on-premises network? Each correct answer presents part of the solution.
NOTE Each correct selection is worth one point.
Your network contains an on-premises Active Directory Domain Services (AD DS) domain.
You have a Microsoft 365 subscription.
You need to recommend a solution to evaluate the security and governance of the domains. The solution must meet the following requirements:
• identify configuration issues and administrative vulnerabilities.
• Minimize effort.
What should you include in the recommendation?
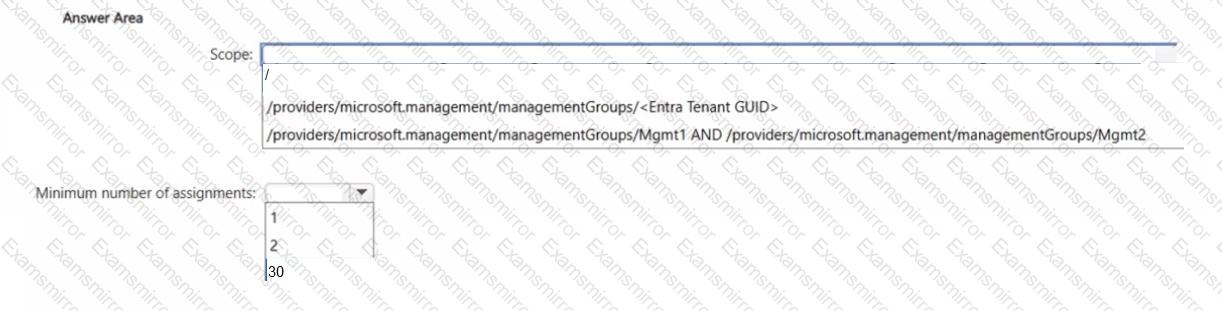
You have a Microsoft Entra tenant named contoso.com. You have 30 Azure subscriptions that are linked to contoso.com. The tenant contains the management groups shown in the following table.
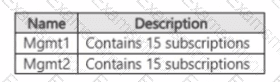
You need to design a governance solution to manage access to all the Azure Storage accounts across the subscriptions. The solution must meet the following requirements:
• Use custom role-based access control (RBAQ to provide granular access to control plane and data plane operations.
• Minimize administrative effort.
At which scope should you assign the roles, and what is the minimum number of assignments per role? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have two on-premises servers named Server! and Server2 that run Windows Server. Server1 contains an app named App1 and is isolated from the internet.
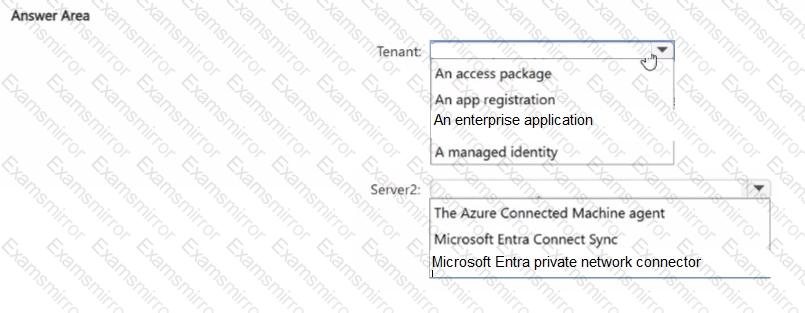
You have a Microsoft Entra tenant
You plan to deploy Global Secure Access to provide remote access to App1.
You need to configure the tenant and Server2 to support the planned deployment. The solution must ensure that when users attempt to access App1, they must authenticate by using their Microsoft Entra credentials.
What should you create in the tenant, and what should you install on Server2? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 subscription that uses Microsoft Defender XDR. The subscription contains 500 devices that are enrolled in Microsoft Intune. The subscription contains 500 users that connect to external software as a service (SaaS) apps by using the devices.
You need to implement a solution that meets the following requirements:
• Allows user access to SaaS apps that Microsoft has identified as low risk.
• Blocks user access to Saas apps that Microsoft has identified as high risk.
Solution: From Microsoft Defender for Cloud Apps, you configure a cloud discovery policy and unsanction risky apps.
Does this meet the goal?
You have an Azure subscription.
You plan to deploy Azure App Services apps by using Azure DevOps.
You need to recommend a solution to ensure that deployed apps maintain compliance with Microsoft cloud security benchmark (MCSB) recommendations.
What should you include in the recommendation?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.