Month End Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = drift75
Pass the Microsoft Certified: Information Security Administrator Associate SC-500 Questions and answers with ExamsMirror
Exam SC-500 Premium Access
View all detail and faqs for the SC-500 exam
0 Students Passed
0% Average Score
0% Same Questions
You have a Microsoft Entra tenant that has the following configurations:
•User consent for applications is disabled.
•Only administrators can grant permissions to applications.
You register an application named App1 that uses delegated Microsoft Graph permissions.
You need to configure App1 to meet the following requirements:
•Enable user sign-ins without interactive consent prompts.
•Enable App1 to access Microsoft Graph on behalf of the signed-in user.
What should you do?
You plan to deploy Microsoft 365 Copilot.
You discover that Copilot can access sensitive information in your Microsoft SharePoint Online libraries.
You need to automatically identify which SharePoint Online content has been shared between all internal users.
What should you create?
You have a hybrid environment that contains the following servers:
•50 Azure virtual machines that run Windows Server 2019
•20 physical, on premises servers that run Windows Server 2019
All the servers use a third-party antivirus solution that must remain active during a phased security rollout
You need to onboard all the servers to Microsoft Defender for Endpoint by using a centralized deployment method. The solution must meet the following requirements:
•Endpoint detection and response (EDR) capabilities must be enabled.
•Antivirus conflicts must be prevented during onboarding.
What should you do on the servers?
You have an Azure subscription that contains the virtual networks shown in the following table.
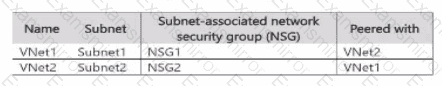
NSG1 and NSG2 both have default rules only.
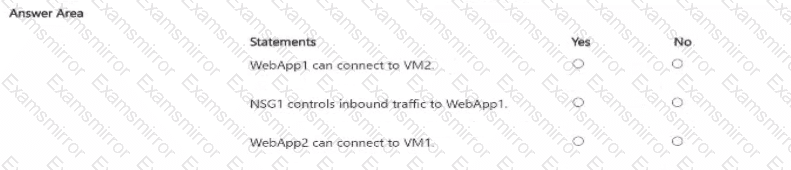
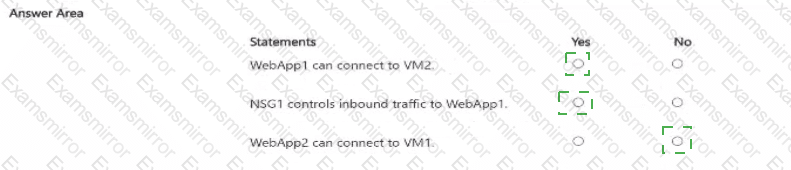
The subscription contains the virtual machines shown in the following table.
You have an Azure subscription named Sub1. Sub1 contains 20 virtual machines that run Windows Server.
Sub1 has the Microsoft Defender for Cloud Defender Cloud Security Posture Management (CSPM) plan enabled.
You need to ensure that all the virtual machines are scanned automatically for known security flaws and misconfigurations.
What should you use?
You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
You have an Azure subscription named Sub1 that contains multiple virtual machines.
You have a Microsoft 365 E5 subscription that contains devices onboarded to Microsoft Defender for Endpoint.
You have an on-premises datacenter that contains multiple servers.
You plan to onboard all existing and future on-premises servers to Azure Arc.
You need to ensure that the Azure Arc-enabled servers are protected by using the same security features as the Microsoft 365 devices immediately after the servers are onboarded. The solution must minimize administrative effort.
What should you do?
You have an Azure subscription named Sub1 that contains a storage account named storage1
Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has on-upload malware scanning enabled for a monthly cap of 10,000 GB per storage account.
You use a Microsoft Sentinel workspace to monitor security events on all Azure resources.
You need to configure storage1 to use a malware scanning cap of 2.000 GB per month.
What should you do?
You use Microsoft Security Copilot.
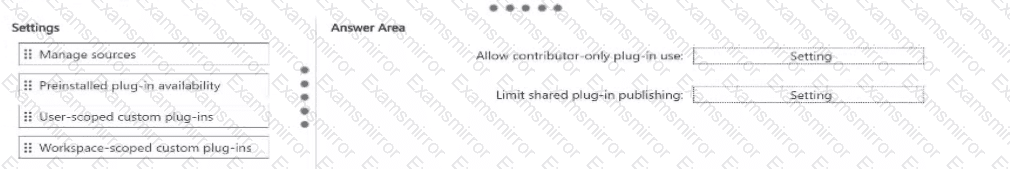
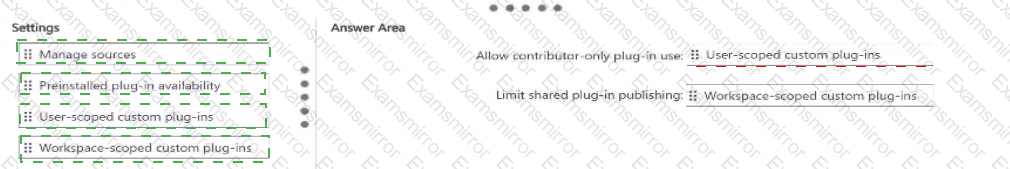
You need to update Plugin settings. the solution must meet the following requirements:
• Allow contributors to use custom plug-ins without affecting either UMTS
• Limit publishing of custom plug-ins for other users to Owners only.
Which Plugin settings option should you configure for each requirement? To answer, drag the appropriate settings lo the correct requirements. Each setting may be used once, more than once., or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have a Microsoft Security Copilot workspace named Workspace1 that is used by Security Operations Center (SOC) analysts and security administrators.
The SOC analysts use only the Security Copilot standalone experience, and the security administrators access Security Copilot from the Microsoft Defender portal.
A new Security Copilot workspace named Workspace2 is created for the security administrators. Workspace2 is assigned a capacity of five security compute units.
You need to ensure that Security Copilot usage for the SOC analysts is allocated to Workspace1 and Security Copilot usage for the security administrators is allocated to Workspace2.
What should you do?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.