Pre-Winter Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = getmirror

Pass the Fortinet Network Security Expert NSE5_FSW_AD-7.6 Questions and answers with ExamsMirror

Practice at least 50% of the questions to maximize your chances of passing.
Exam NSE5_FSW_AD-7.6 Premium Access

View all detail and faqs for the NSE5_FSW_AD-7.6 exam


514 Students Passed

86% Average Score

92% Same Questions
Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions
Questions # 11:

Which statement about the quarantine VLAN on FortiSwitch is true?

Options:

A.

Quarantine VLAN has no DHCP server

B.

Users who fail 802.1X authentication can be placed on the quarantine VLAN.

C.

It is only used for quarantined devices if global setting is set to quarantine by VLAN.

D.

FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.

Questions # 12:

Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?

Options:

A.

lt is a scalable and secure solution in comparison to other Layer 2 security measures.

B.

FortiSwitch uses only the Ethernet type to assign traffic to VLANs.

C.

It provides benefits that can be obtained when using 802.1X authentication.

D.

Endpoints are required to use the same FortiSwitch port to remain members of the VLAN.

Questions # 13:

Exhibit.

port1 and port2 are the only ports configured with the same native VLAN 10.

What are two reasons that can trigger port1 to shut down? (Choose two.)

Options:

A.

port1 was shut down by loop guard protection.

B.

STP triggered a loop and applied loop guard protection on port1.

C.

An endpoint sent a BPDU on port1 that it received from another interface.

D.

Loop guard frame sourced from port1 was received on port1.

Questions # 14:

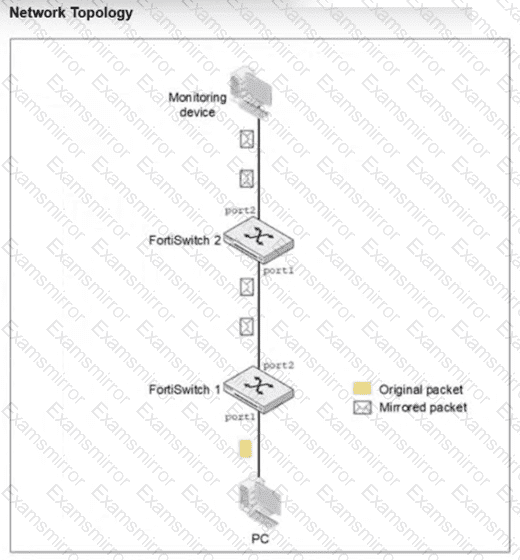
Refer to the exhibit.

Question # 14

You configured Switched Port Analyzer (SPAN) to monitor traffic from a source port on FortiSwitch 1, but the monitoring device is connected to FortiSwitch 2. After port mirroring configuration on FortiSwitch 1, the monitoring device is not receiving any mirrored traffic.

What is the most likely reason the mirrored traffic is not reaching the monitoring device? (Choose one answer)

Options:

A.

SPAN does not support forwarding mirrored traffic across multiple switches.

B.

SPAN traffic must be filtered with an access control list (ACL).

C.

The SPAN session must be restarted after configuration.

D.

The monitoring device must use a management IP in the same subnet.

Questions # 15:

Exhibit.

port24 is the only uplink port connected to the network where access to FortiSwitch management services is possible. However, FortiSwitch is still not accessible on the management interface. Which two actions should you take to fix the issue and access FortiSwitch? (Choose two.)

Options:

A.

You must add port24 native VLAN as an allowed VLAN on internal.

B.

You must add VLAN ID 200 to the allowed VLANS on internal.

C.

You must allow VLAN ID 4094 on port24, if management traffic is tagged.

D.

You should use VLAN ID 4094 as the native VLAN on port24.

Questions # 16:

Which QoS mechanism maps packets with specific CoS or DSCP markings to an egress queue?

Options:

A.

Queuing for egress traffic

B.

Classification for ingress traffic

C.

Rate limiting for egress traffic

D.

Marking for ingress traffic

Questions # 17:

On supported FortiSwitch models, which access control list (ACL) stage is recommended for applying actions before the switch performs any layer 2 or layer 3 processing? (Choose one answer)

Options:

A.

Ingress

B.

Forwarding

C.

Egress

D.

Prelookup

Questions # 18:

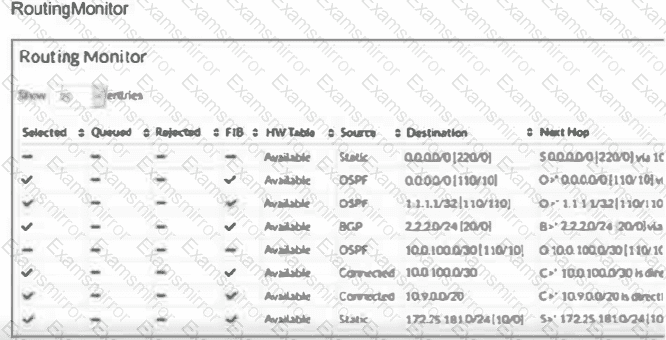
Exhibit.

Question # 18

Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)

Options:

A.

These two routes have a higher administrative distance value available to the destination networks.

B.

These two routes will become primary, if the best routes are removed.

C.

These two routes will be used as load-balancing routes.

D.

These two routes are available in the hardware routing table.

Questions # 19:

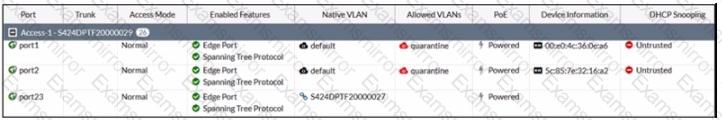
Refer to the exhibit.

Question # 19

The exhibit shows the current status of the ports on the managed FortiSwitch. Access-1.

Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?

Options:

A.

port23 is configured as the dedicated management interface.

B.

Ports connected to adjacent FortiSwitch devices show their serial number as the native VLAN.

C.

port23 is a member of a trunk that uses the Access-1 FortiSwitch serial number as the name of the trunk.

D.

A standalone switch with the shown serial number is connected on port23.

Questions # 20:

(Full question statement start from here)

Refer to the exhibits.
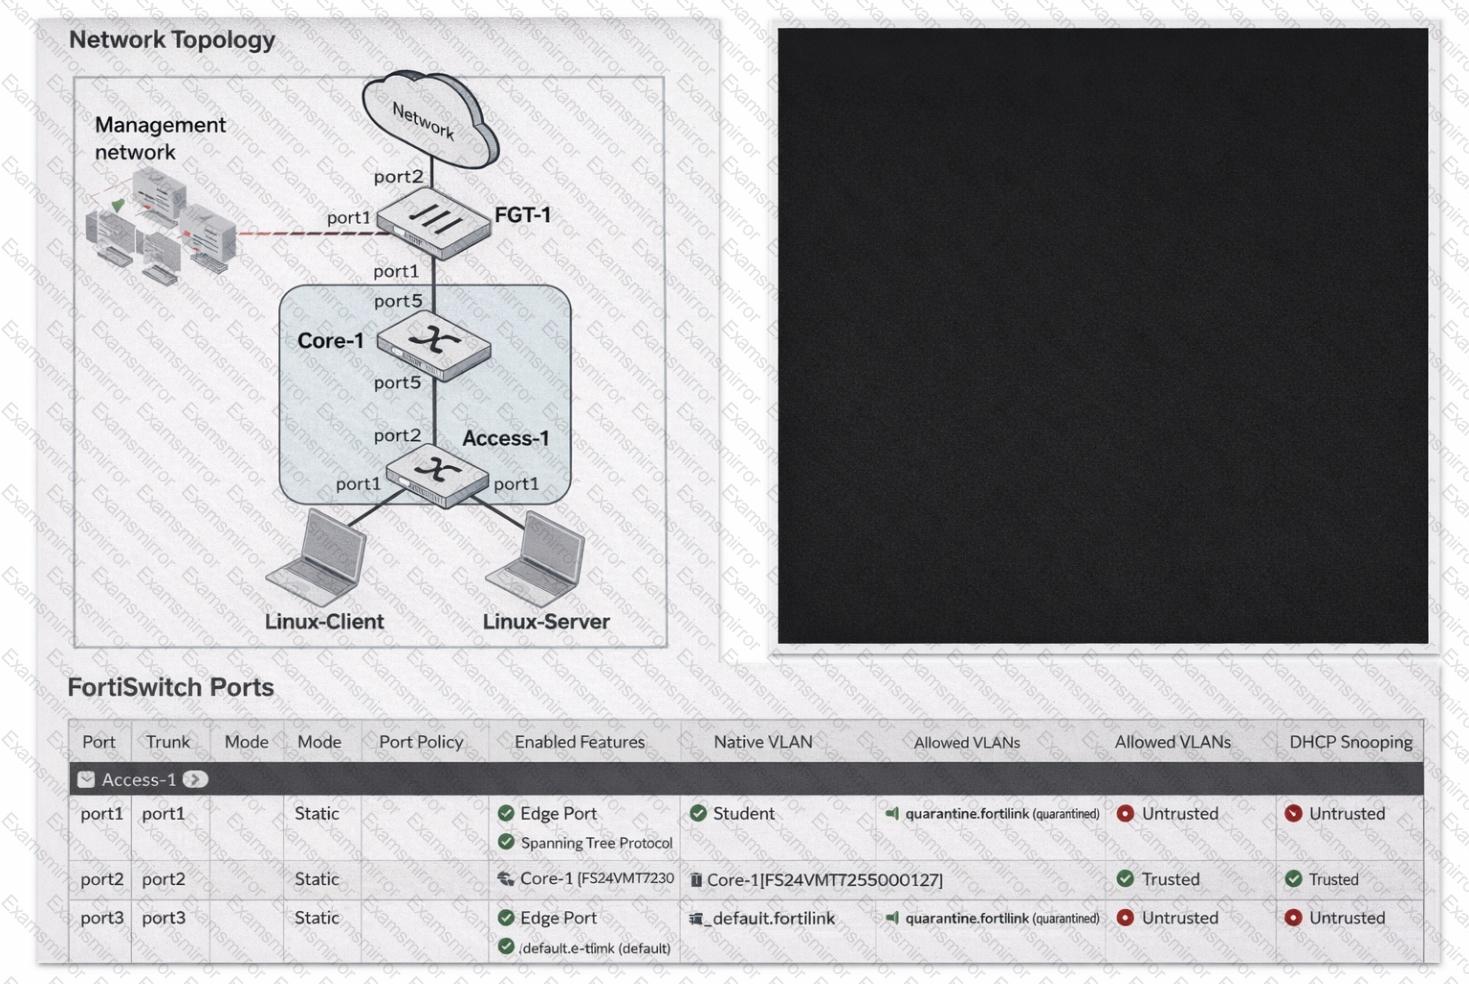
Question # 20

You enable Dynamic Host Configuration Protocol (DHCP) snooping on the VLAN,Student. The Linux-Client VM sends DHCP requests, and tcpdump confirms the broadcasts. However, the Linux-Server VM, acting as a DHCP server, receives no DHCP traffic. What is the most likely cause of this intra-VLAN traffic being blocked? (Choose one answer)

Options:

A.

The DHCP requests are being sent on the wrong VLAN.

B.

Port1 is configured as an untrusted port.

C.

Port4 is not configured as a trusted port.

D.

The Student VLAN must be configured as an allowed VLAN on port1.

Viewing page 2 out of 4 pages
Viewing questions 11-20 out of questions
TOP CODES

TOP CODES

Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.