Black Friday Grand offer - Upto 75% off - Ends in 0d 00h 00m 00s - Coupon code = drift75
Pass the Microsoft Certified: Information Security Administrator Associate SC-500 Questions and answers with ExamsMirror
Exam SC-500 Premium Access
View all detail and faqs for the SC-500 exam
0 Students Passed
0% Average Score
0% Same Questions
You have a network security group (NSG) bound to an Azure subnet
You run Get-AzNetworkSecurityRuleConf ig and receive the output shown in the following exhibit
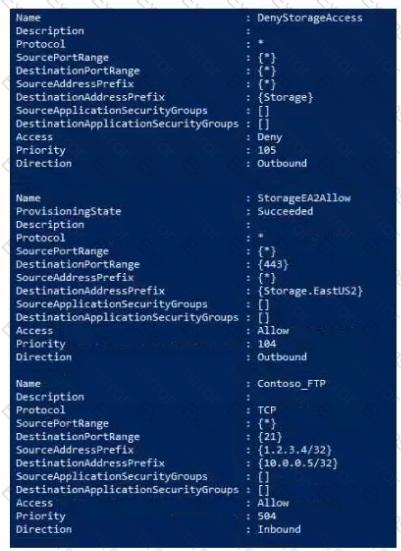
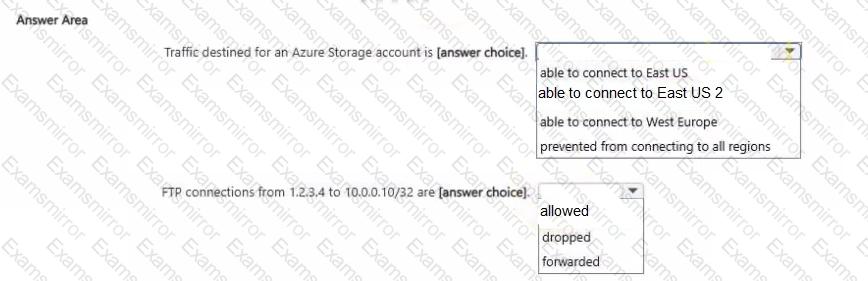
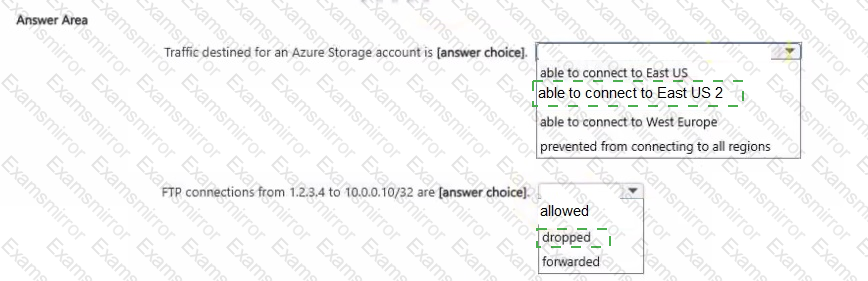
Use the drop-down menus to select the answer choice that completes each statement based on the information presented in the graphic.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that contains the virtual networks shown in the following table.
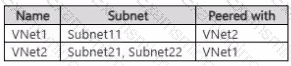
The subscription contains the virtual machines shown in the following table.
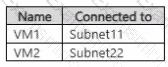
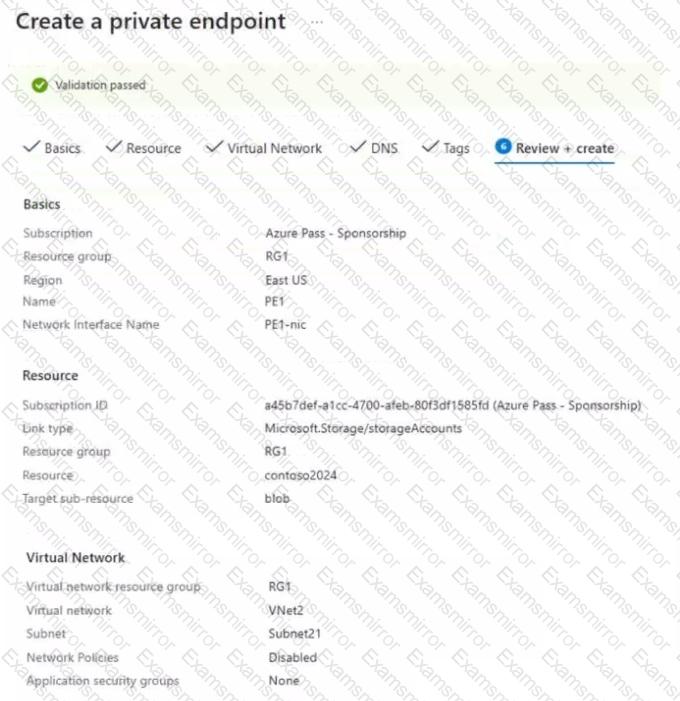
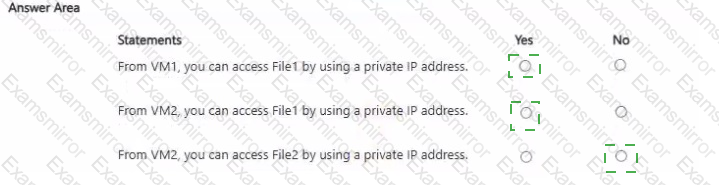
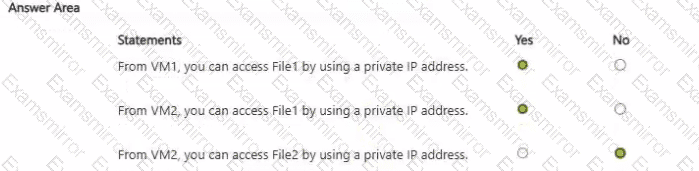
You have a storage account named contoso2024 that contains the following resources:
• A container named contained that contains a file named File1
• A file share named share1 that contains a file named File2
You create a private endpoint for contoso2024 as shown in the following exhibit.
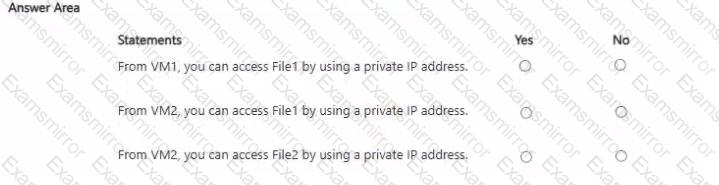
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE Each correct selection is worth one point.
You have an Azure subscription that contains a resource group named RG1 and has Microsoft Defender for Cloud enabled.
You connect an Amazon Web Services (AWS) account to Defender for Cloud by creating the AWS connector in RG1.
You have a Microsoft Entra group named Group1 that contains the user accounts of the security analysts at your company.
You need to ensure that the members of Group1 can view multicloud recommendations and security alerts for the connected AWS account. The solution must follow the principle of least privilege.
Which role should you assign to Group1 for RG1?
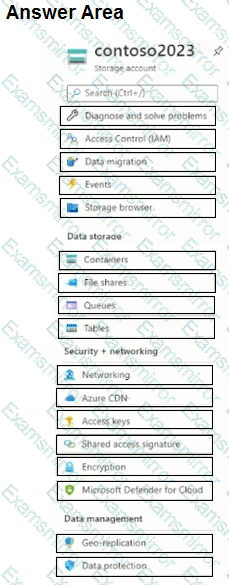
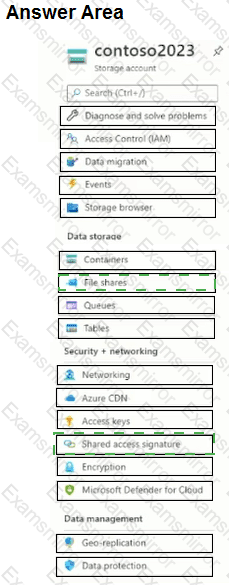
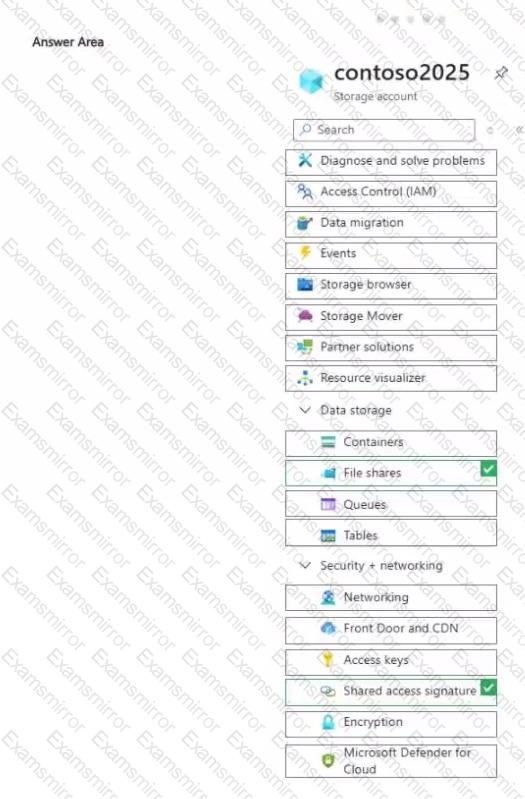
You have an Azure subscription that contains a storage account named contoso2025. You need to perform the following tasks:
• Verify that identity-based authentication over SMB is enabled.
• Only grant users access to contoso2025 in the year 2025.
Which two settings should you use? To answer, select the appropriate settings in the answer area.
NOTE Each correct selection is worth one point.
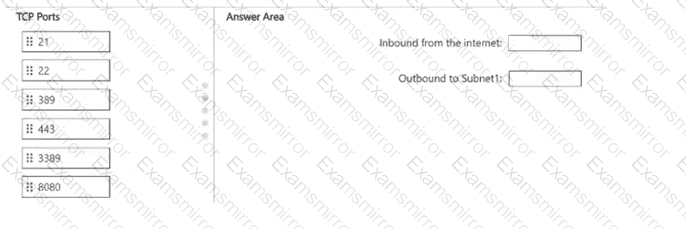
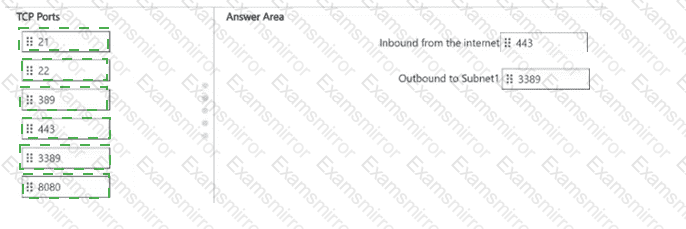
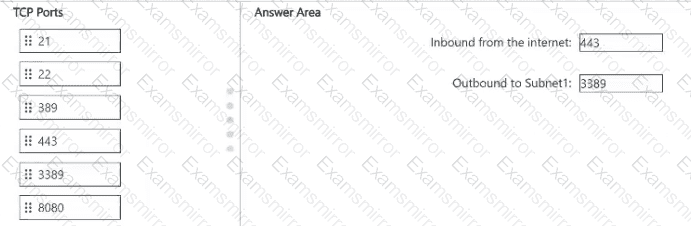
You have an Azure virtual network named VNet1 that contains an Azure Bastion Subnet. VNet1 contains a subnet named Subnet1 Subnet1 contains multiple virtual machines.
You plan to deploy Azure Bastion to provide secure RDP access to the virtual machines on Subnet1. You associate a network security group (NSG) named NSG1 to Azure Bastion Subnet.
You need to configure rules for NSG1. The solution must meet the following requirements:
•Allow required inbound access to Azure Bastion from the internet.
•Allow user access to the virtual machines by using Azure Bastion.
Which TCP ports should you allow for the NSG1 rules? To answer, drag the appropriate ports to the correct rules. Each port may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
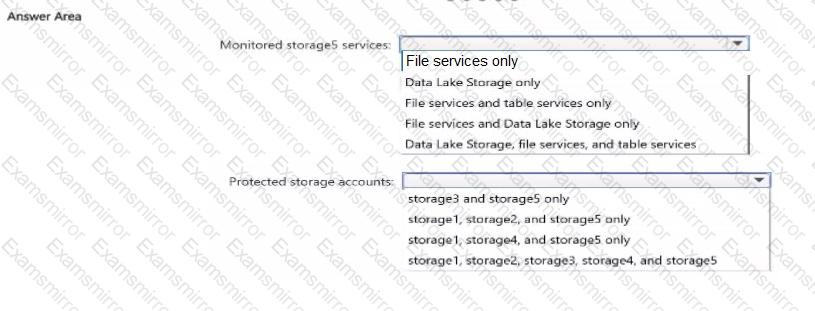
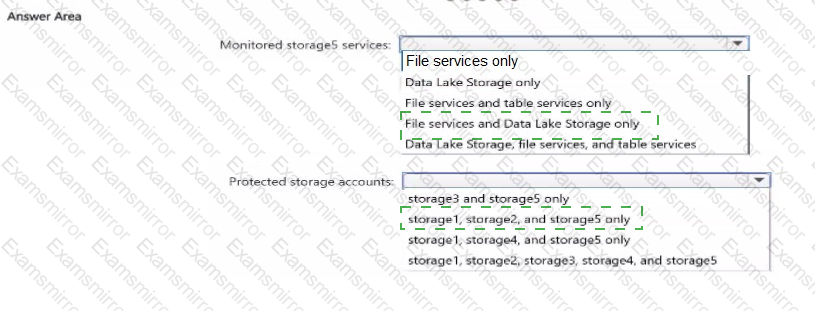
You have an Azure Subscription that contains the storage accounts shown in the following table.
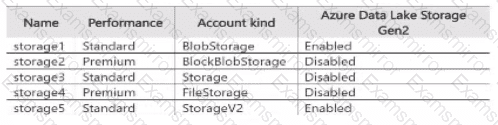
You enable Microsoft Defender for Storage.
Which storage services of storage5 are monitored by Microsoft for Storage which storage accounts are protected by.
You have an Azure subscription that contains a managed identity named Identity1 and the Azure key vaults shown in the following table.
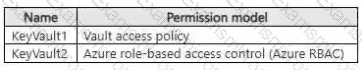
KeyVault1 contains an access policy that grants Identity 1 the following key permissions;
• Get
• List
• Wrap
• Unwrap
You need to provide identity1 with the same permissions for KeyVault2. The solution must use the principle of least privilege. Which role should you assign to identity1?
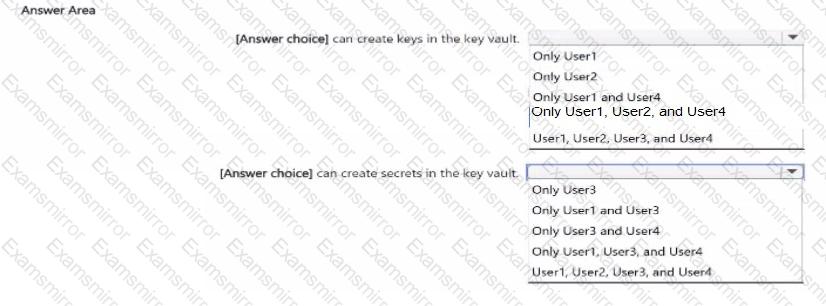
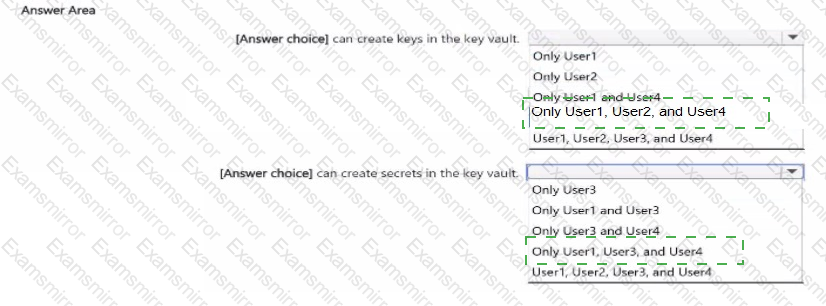
You have an Azure subscription that contains an Azure Key vault. The role assignments for the vault are shown in the following.
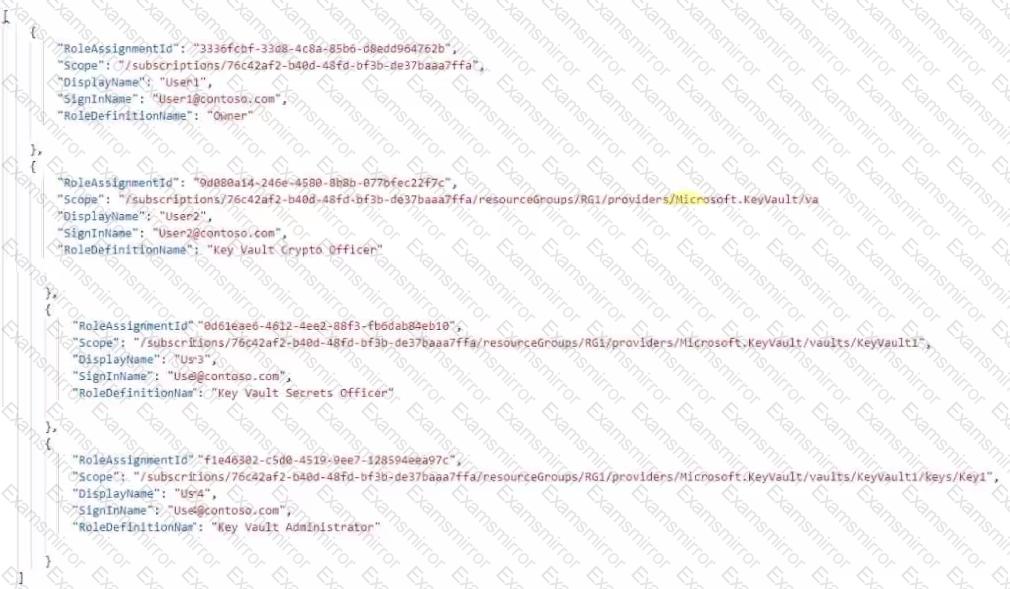
NOTE: Each correct select is worth one point.
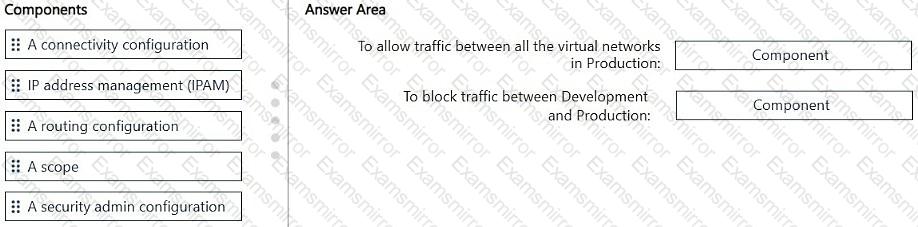
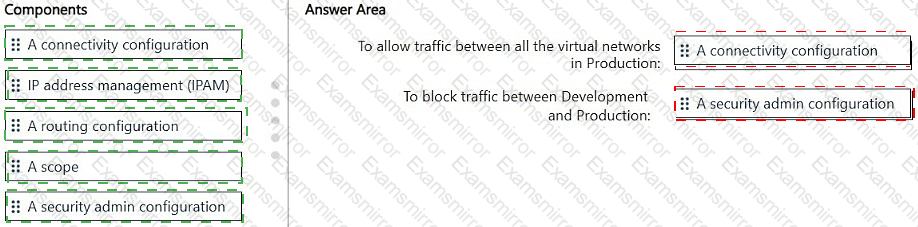
You use Azure Virtual Network Manager to manage multiple virtual networks organized into two network groups named Production and Development.
You need to configure Virtual Network Manager to meet the following requirements:
Allow traffic between all the virtual networks in Production.
Block traffic between Development and Production.
What should you use for each requirement? To answer, drag the components to the correct requirements. Each component may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
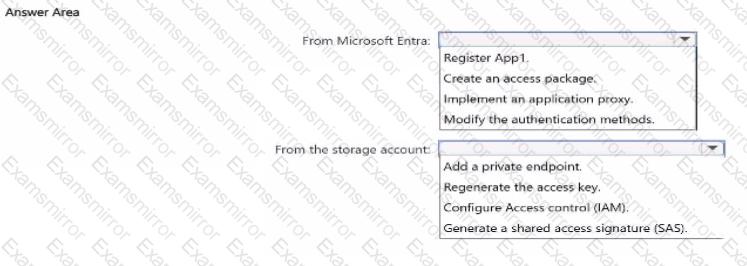
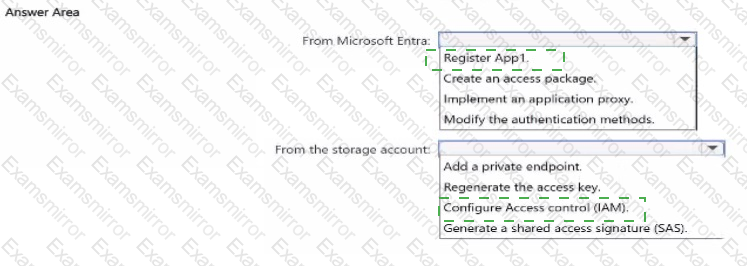
You have an Azure Storage account that contains a blob container named container 1 and a client application named App1. You need to enable App1 access to container1 by using Microsoft Entra authentication. What should you do ' To answer, select the appropriate options in the answer area. NOTE: Each correct selection is worth one point.

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.