Pre-Winter Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = getmirror

Pass the Splunk Cybersecurity Defense Analyst SPLK-5002 Questions and answers with ExamsMirror

Practice at least 50% of the questions to maximize your chances of passing.
Exam SPLK-5002 Premium Access

View all detail and faqs for the SPLK-5002 exam


762 Students Passed

84% Average Score

94% Same Questions
Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions
Questions # 21:

Risk scores are associated with how many levels of risk in Enterprise Security by default?

Options:

A.

(4) Info, Medium, High, Critical

B.

(3) Low, Medium, High

C.

(5) Info, Low, Medium, High, Critical

D.

(6) Info, Low, Medium, High, Critical, Unknown

Questions # 22:

What must be configured as a setting in a correlation search for a notable to be generated?

Options:

A.

A SOAR playbook must execute against the notable.

B.

Nothing; the correlation search will generate a notable automatically as an outcome.

C.

An Adaptive Response Action must be configured to enable the notable generation.

D.

The search must end with a | notable SPL command.

Questions # 23:

Which of the following is a methodology to help prevent malicious lateral movement?

Options:

A.

Breakglass

B.

Lockheed Martin Cyber Kill Chain®

C.

MITRE ATT & CK®

D.

Zero Trust

Questions # 24:

An engineer wants to track and report on all authentication to corporate assets and wants to prioritize critical assets without significantly increasing the number of findings created. What process could be used to accomplish this goal?

Options:

A.

Decrease the risk score of non-critical assets in all existing detections.

B.

Add all access attempts to the Risk Index and increase criticality of critical assets.

C.

Add the critical assets to the risk data model.

D.

Determine a general risk rule for all access attempts to all assets, and then increase the Risk Factor for critical assets.

Questions # 25:

In Enterprise Security, what is the name of the threat intelligence lookup pertaining to files?

Options:

A.

file_hash

B.

file_intel

C.

user_intel

D.

user_hash

Questions # 26:

The SOC notices over the course of an investigation there are numerous logs similar to the following:

UDP: query: reallybad.c2.com IN A response: SERVFAIL

What detection should be created to alert on this behavior for the future?

Options:

A.

Excessive DNS Failures

B.

Excessive Authentication Failures

C.

Excessive Network Failures

D.

Excessive Endpoint Failures

Questions # 27:

Based on the provided screenshot, it ' s discovered that different machines or accounts have been associated with the shown threat objects.
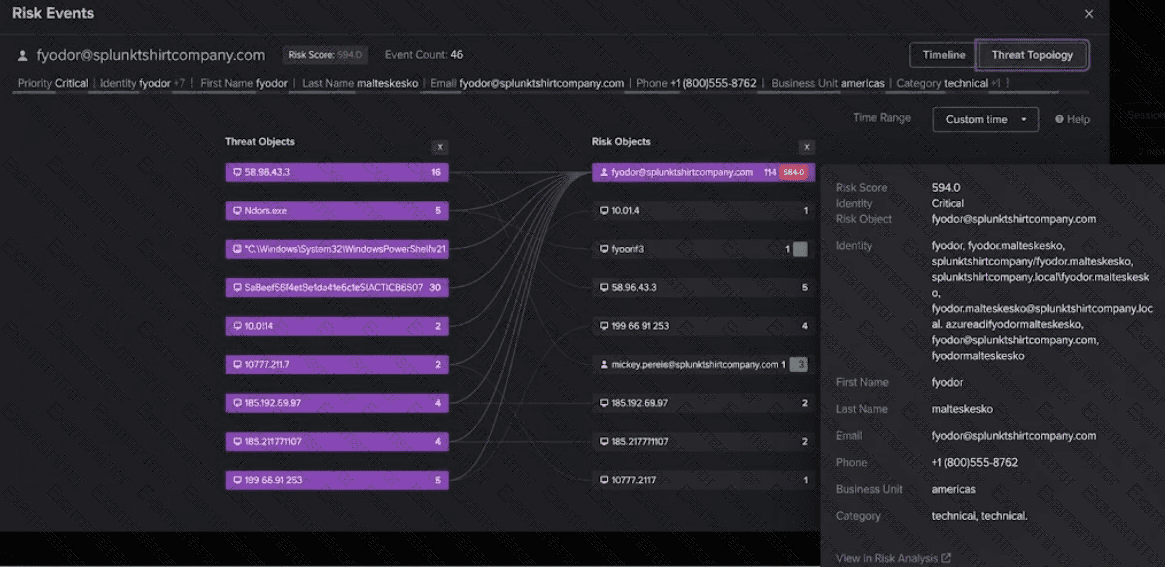
Question # 27

Enterprise Security has identified that these machines and accounts all point back to one owner - Fyodor. Which two frameworks in ES are responsible for programmatically associating this information together?

Options:

A.

Threat Intelligence, Assets & Identities

B.

Risk, Incident Review

C.

Risk, Assets & Identities

D.

Threat Intelligence, Risk

Questions # 28:

When should a detection be reviewed or retuned after deployment?

Options:

A.

Every 30 days.

B.

Only if it has generated a large amount of false positives.

C.

As defined by the established detection lifecycle.

D.

Only if it hasn ' t generated a finding after several weeks.

Questions # 29:

Which of the following should an engineer do as they evaluate their Threat Detection and Incident Response lifecycle?

Options:

A.

Focus efforts on the least impactful threat vectors.

B.

Use the MITRE ATT & CK Framework to evaluate the organization ' s risk appetite.

C.

Evaluate the threat process lifecycle solely from predefined technical profiles.

D.

Evaluate the threat process lifecycle based on contextual business and industry knowledge.

Questions # 30:

What is a key feature of effective security reports for stakeholders?

Options:

A.

High-level summaries with actionable insights

B.

Detailed event logs for every incident

C.

Exclusively technical details for IT teams

D.

Excluding compliance-related metrics

Viewing page 3 out of 4 pages
Viewing questions 21-30 out of questions
TOP CODES

TOP CODES

Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.