Halloween Sale Special Limited Time 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = drift75

Pass the Cisco CCNP Security 350-701 Questions and answers with ExamsMirror

Practice at least 50% of the questions to maximize your chances of passing.
Exam 350-701 Premium Access

View all detail and faqs for the 350-701 exam


764 Students Passed

88% Average Score

97% Same Questions
Viewing page 16 out of 17 pages
Viewing questions 226-240 out of questions
Questions # 226:

An administrator is adding a new switch onto the network and has configured AAA for network access control. When testing the configuration, the RADIUS authenticates to Cisco ISE but is being rejected. Why is the ip radius source-interface command needed for this configuration?

Options:

A.

Only requests that originate from a configured NAS IP are accepted by a RADIUS server

B.

The RADIUS authentication key is transmitted only from the defined RADIUS source interface

C.

RADIUS requests are generated only by a router if a RADIUS source interface is defined.

D.

Encrypted RADIUS authentication requires the RADIUS source interface be defined

Questions # 227:

What is a characteristic of an EDR solution and not of an EPP solution?
Options:

A.

stops all ransomware attacks

B.

retrospective analysis

C.

decrypts SSL traffic for better visibility

D.

performs signature-based detection

Questions # 228:

Question # 228

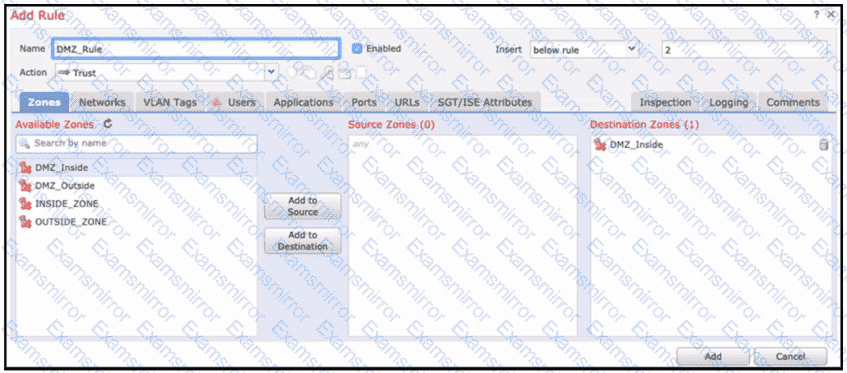
Refer to the exhibit. When configuring this access control rule in Cisco FMC, what happens with the traffic destined to the DMZ_inside zone once the configuration is deployed?

Options:

A.

All traffic from any zone will be allowed to the DMZ_inside zone only after inspection.

B.

No traffic will be allowed through to the DMZ_inside zone regardless of if it ' s trusted or not.

C.

No traffic will be allowed through to the DMZ_inside zone unless it ' s already trusted.

D.

All traffic from any zone to the DMZ_inside zone will be permitted with no further inspection.

Questions # 229:

An engineer is adding a Cisco router to an existing environment. NTP authentication is configured on all devices in the environment with the command ntp authentication-key 1 md5 Clsc427128380. There are two routers on the network that are configured as NTP servers for redundancy, 192.168.1.110 and 192.168.1.111. 192.168.1.110 is configured as the authoritative time source. What command must be configured on the new router to use 192.168.1.110 as its primary time source without the new router attempting to offer time to existing devices?

Options:

A.

ntp server 192.168.1.110 primary key 1

B.

ntp peer 192.168.1.110 prefer key 1

C.

ntp server 192.168.1.110 key 1 prefer

D.

ntp peer 192.168.1.110 key 1 primary

Questions # 230:

Which two features of Cisco DNA Center are used in a Software Defined Network solution? (Choose two)

Options:

A.

accounting

B.

assurance

C.

automation

D.

authentication

E.

encryption

Questions # 231:

Which algorithm is an NGE hash function?

Options:

A.

HMAC

B.

SHA-1

C.

MD5

D.

SISHA-2

Questions # 232:

Which approach reduces the risk of social engineering attacks?

Options:

A.

Enabling NAT traversal for endpoint management

B.

Conducting regular security awareness training for all users

C.

Using port security to limit DHCP spoofing

D.

Restricting outbound TCP traffic to known subnets

Questions # 233:

Refer to the exhibit.

Question # 233

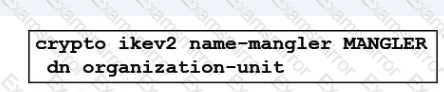
An engineer is implementing a certificate based VPN. What is the result of the existing configuration?

Options:

A.

The OU of the IKEv2 peer certificate is used as the identity when matching an IKEv2 authorization policy.

B.

Only an IKEv2 peer that has an OU certificate attribute set to MANGLER establishes an IKEv2 SA successfully

C.

The OU of the IKEv2 peer certificate is encrypted when the OU is set to MANGLER

D.

The OU of the IKEv2 peer certificate is set to MANGLER

Questions # 234:

Which policy does a Cisco Secure Web Appliance use to block or monitor URL requests based on the reputation score?

Options:

A.

Encryption

B.

Enforcement Security

C.

Cisco Data Security

D.

Outbound Malware Scanning

Questions # 235:

An engineer wants to automatically assign endpoints that have a specific OUI into a new endpoint group. Which

probe must be enabled for this type of profiling to work?

Options:

A.

NetFlow

B.

NMAP

C.

SNMP

D.

DHCP

Questions # 236:

An engineer configures new features within the Cisco Umbrella dashboard and wants to identify and proxy traffic that is categorized as risky domains and may contain safe and malicious content. Which action accomplishes these objectives?

Options:

A.

Configure URL filtering within Cisco Umbrella to track the URLs and proxy the requests for those categories and below.

B.

Configure intelligent proxy within Cisco Umbrella to intercept and proxy the requests for only those categories.

C.

Upload the threat intelligence database to Cisco Umbrella for the most current information on reputations and to have the destination lists block them.

D.

Create a new site within Cisco Umbrella to block requests from those categories so they can be sent to the proxy device.

Questions # 237:

An organization is implementing AAA for their users. They need to ensure that authorization is verified for every command that is being entered by the network administrator. Which protocol must be configured in order to provide this capability?

Options:

A.

EAPOL

B.

SSH

C.

RADIUS

D.

TACACS+

Questions # 238:

A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?

Options:

A.

Configure the Calling-Station-ID attribute for CoA session identification.

B.

Apply the Message-Authenticator attribute for endpoint session lookup.

C.

Implement the Acct-Session-ID attribute for matching the active session.

D.

Use the NAS-Port-ID attribute for the CoA disconnect request.

Questions # 239:

Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?

Options:

A.

NTP

B.

syslog

C.

SNMP

D.

NetFlow

Questions # 240:

What is a benefit of using telemetry over SNMP to configure new routers for monitoring purposes?

Options:

A.

Telemetry uses a pull mehod, which makes it more reliable than SNMP

B.

Telemetry uses push and pull, which makes it more scalable than SNMP

C.

Telemetry uses push and pull which makes it more secure than SNMP

D.

Telemetry uses a push method which makes it faster than SNMP

Viewing page 16 out of 17 pages
Viewing questions 226-240 out of questions
TOP CODES

TOP CODES

Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.