Pre-Winter Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = getmirror
Pass the CompTIA CySA+ CS0-004 Questions and answers with ExamsMirror
Exam CS0-004 Premium Access
View all detail and faqs for the CS0-004 exam
0 Students Passed
0% Average Score
0% Same Questions
An incident response team identifies a malicious uniform resource locator (URL) associated with a required business process and performs the following activities:
• Access to the URL has been restricted only to the necessary users through firewall rules and Cloud Security Group rules.
• Additional monitoring has been enabled for traffic related to that site and the allowed users.
• All application servers that need to access that site have been patched with the latest security and software updates.
• Application owners have been notified of the severity and need to remediate this reported issue.
Which of the following best describes the overall mitigation the security team is performing?
Which of the following will inhibit remediation when attempting to resolve a vulnerability?
A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team.
The analyst must:
Identify Linux systems that have successful and unsuccessful logins with username "User1".
Create an output report named "linux-events" of all the events to a flat file.
The analyst issues the following console command:
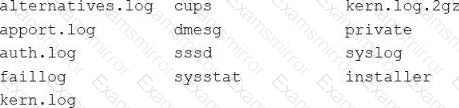
ls /var/log/
The shortened output of the command is below:
Which of the following commands should the analyst use to meet the report output requirements?
Multiple users report unexpected mouse movements and terminal windows opening.
An analyst reviewing the network traffic logs observes the following:
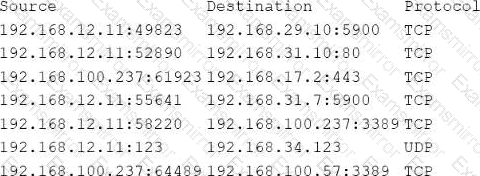
Which of the following is the most likely reason for the reported symptoms?
Which of the following contains stakeholder contact information for incident response reporting?
Which of the following phases of the incident response process will permanently remove an attacker’s access to corporate resources?
A vulnerability analyst conducts a web application scan on an asset sitting behind a load balancer configured as a pass through:
http://10.203.20.10
The analyst launches the Zed Attack Proxy (ZAP) utility, conducts a scan, and receives the following alert:
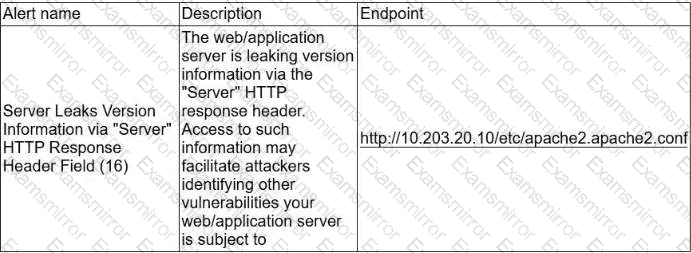
Which of the following should the analyst propose as a remediation to the finding while keeping the site operational?
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network.
Which of the following artifacts should the analyst collect first?
A vendor releases details of a new vulnerability. When an analyst reviews the scheduled scans, no vulnerabilities are identified. The vulnerability is only discovered after a configuration change.
Which of the following scan types did the analyst configure?
A cybersecurity analyst requests a paid subscription to a threat intelligence feed relevant to a company's industry.
Which of the following best describes this type of feed?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.