Pre-Winter Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code = getmirror
Pass the CompTIA CySA+ CS0-004 Questions and answers with ExamsMirror
Exam CS0-004 Premium Access
View all detail and faqs for the CS0-004 exam
0 Students Passed
0% Average Score
0% Same Questions
A security analyst runs an Nmap scan against a host with multiple open ports using the following command:
nmap 10.10.10.1 -p-
The following output is obtained after the scan:
Starting Nmap 7.95 ( https://nmap.org ) at 2025-07-15 15:55 UTC
Note: Host seems down.
Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds
Which of the following is the most accurate way to scan the target IP for open ports?
An analyst needs to perform a baseline security evaluation of the company's cloud infrastructure.
Which of the following tools is most appropriate for this task?
A systems administrator is reviewing the output of a vulnerability scan.
INSTRUCTIONS -
Review the information in each tab.
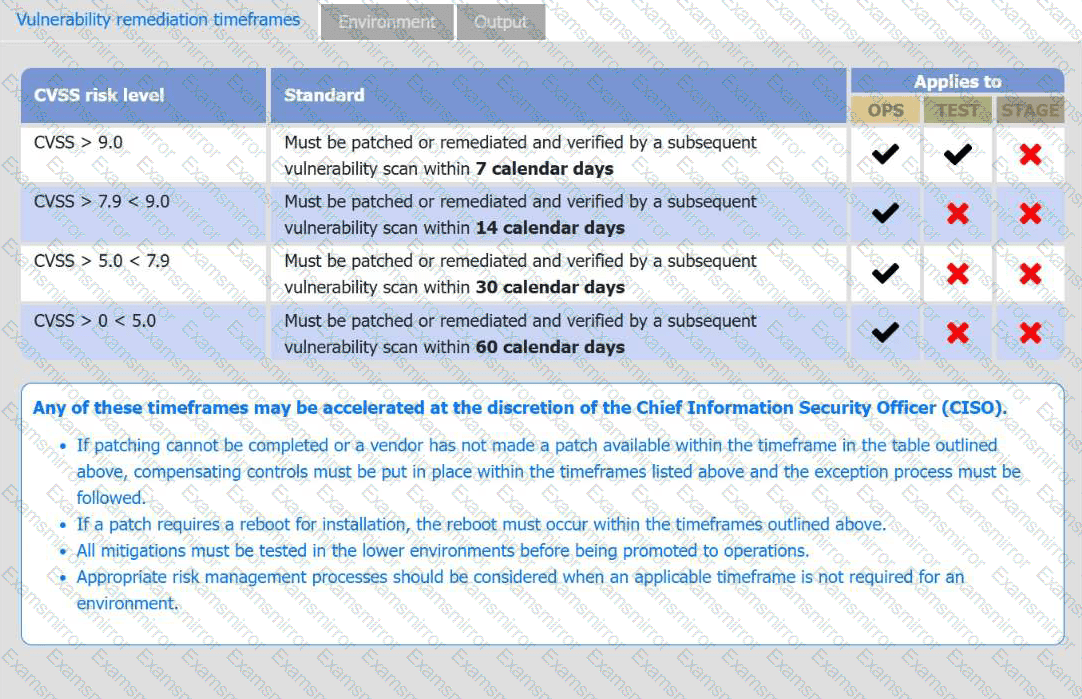
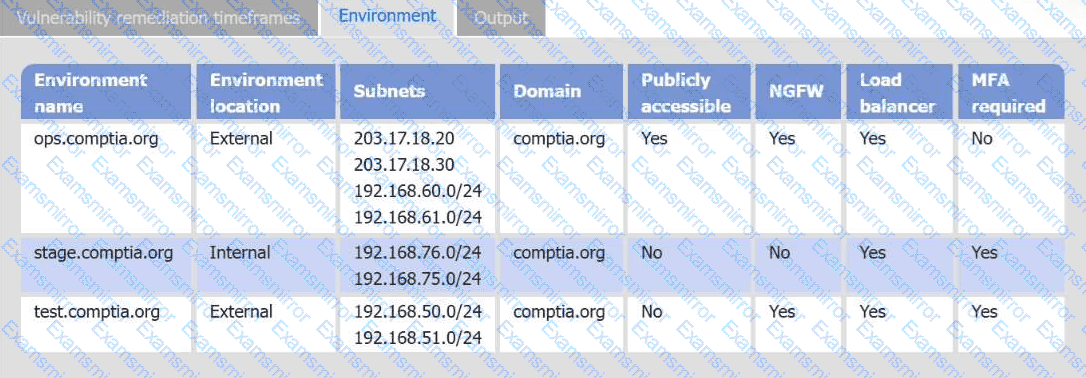
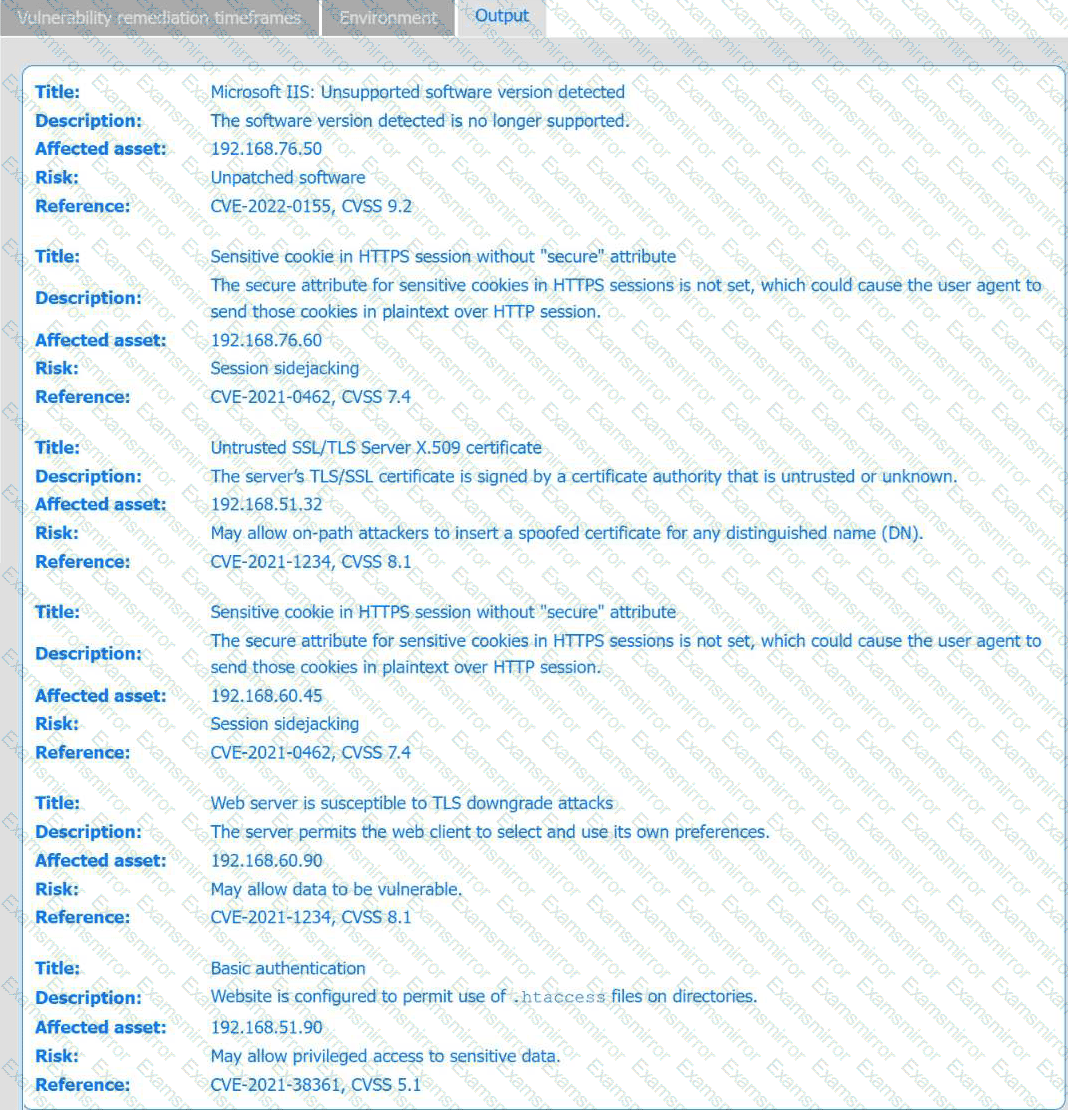
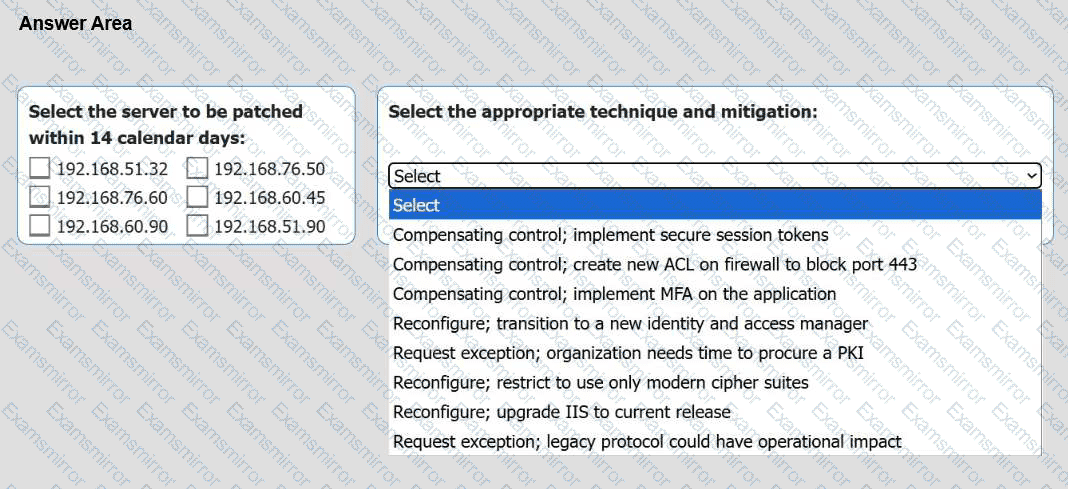
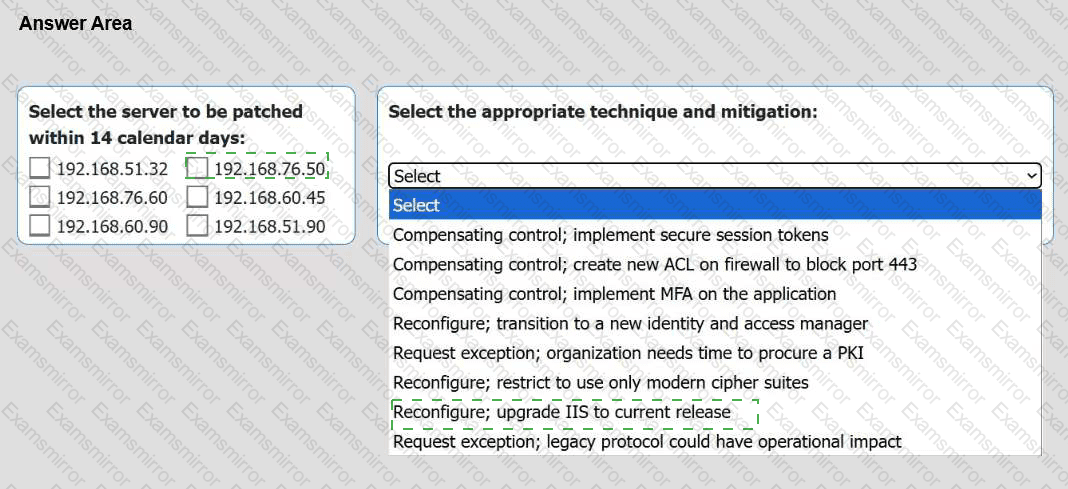
Based on the organization’s environment architecture and remediation standards, select the server to be patched within 14 days and select the appropriate technique and mitigation.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
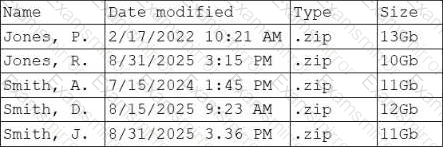
Which of the following actions should the analyst take first?
A public threat intelligence report includes indicators of compromise (IoCs) for threat actors. The threat actors are exploiting a zero-day vulnerability that the vendor has not fixed.
Which of the following techniques should be used until a patch is available?
The Chief Information Officer (CIO) is requiring users to phase out a legacy system that no longer receives security updates because the system will be decommissioned soon.
Which of the following risk management strategies is the CIO using?
There is an alert coming from the security information and event management system.
Which of the following is the first task an analyst should complete?
Which of the following allows an organization to leverage AI in various forms while protecting business objectives and data?
Which of the following is the most likely reason an organization might implement compensating controls?
An analyst reviews the following system logs from a recent breach attempt:
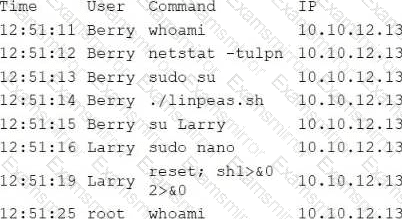
Which of the following techniques did the attacker attempt to use?

TOP CODES
Top selling exam codes in the certification world, popular, in demand and updated to help you pass on the first try.